
Ideas for
your next move.
Practical thinking for teams building software, securing systems and operating modern infrastructure. Explore our engineering field notes.
206 insights · Page 2 of 18
 ENGINEERING JOURNAL ↗
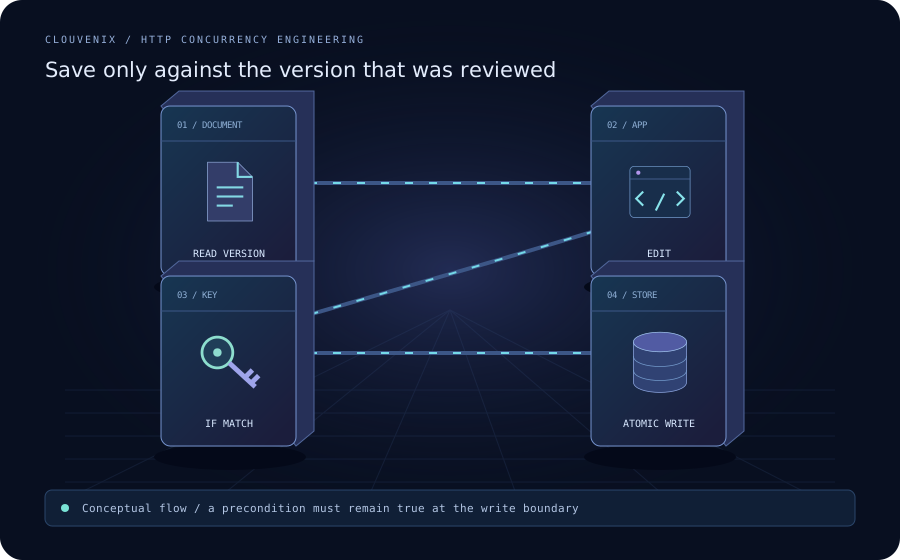
HTTP conditional writes: prevent silent lost updates
Protect concurrent edits with strong validators and atomic conditional writes, then give users a safe conflict-resolution path instead of silently overwriting newer work.
Read field note ↗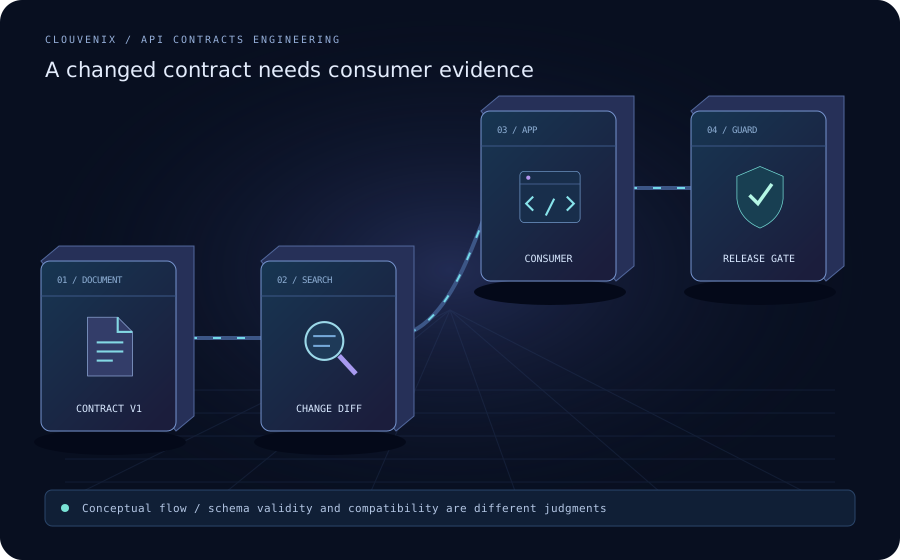 ENGINEERING JOURNAL ↗
OpenAPI changes: test consumer compatibility before release
Review API contract changes across requests, responses and error behavior, then exercise real consumer fixtures instead of assuming a valid OpenAPI document is compatible.
Read field note ↗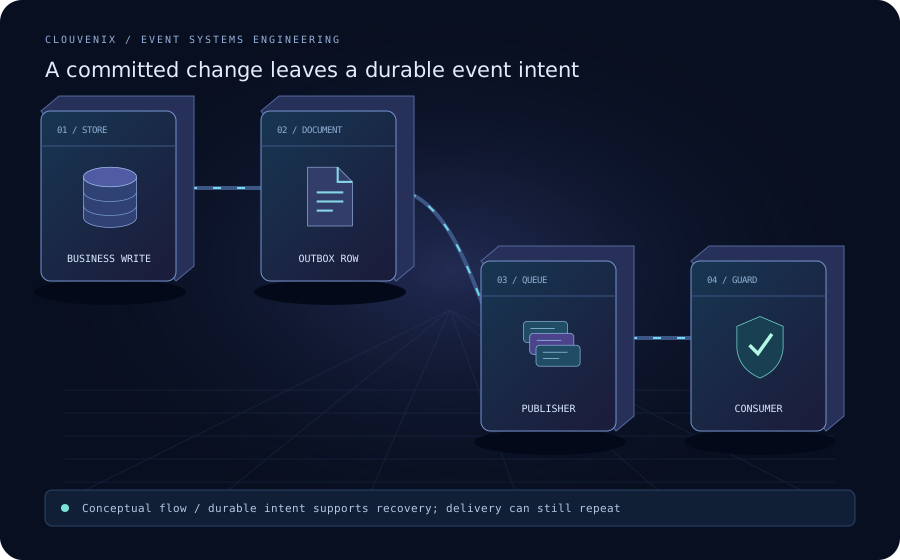 ENGINEERING JOURNAL ↗
Transactional outbox: recover the database-to-message boundary
Use a transactional outbox to track database changes and pending notifications together, then verify publisher recovery, duplicate delivery and consumer idempotency.
Read field note ↗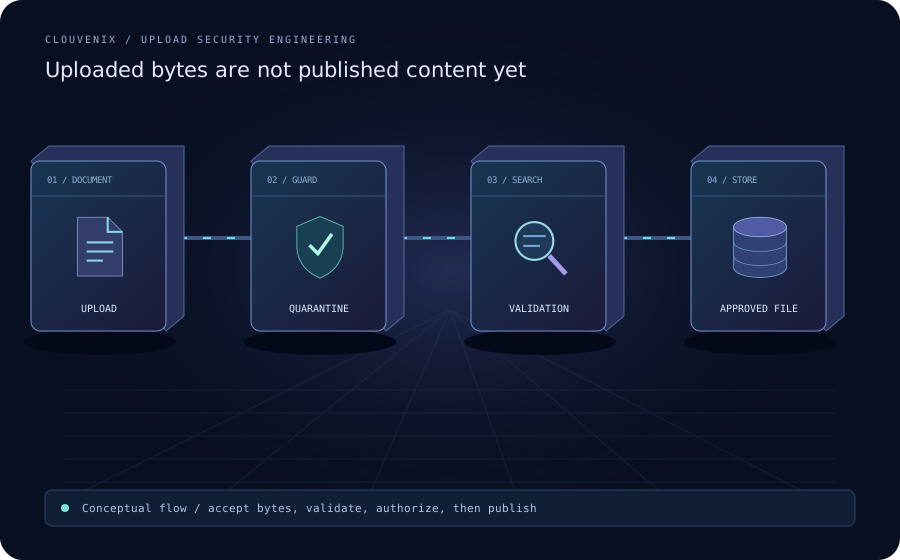 ENGINEERING JOURNAL ↗
Application uploads: quarantine before publication
Build an upload lifecycle with size limits, content validation, private quarantine and authorized release so a successful transfer does not mean a file is safe to publish.
Read field note ↗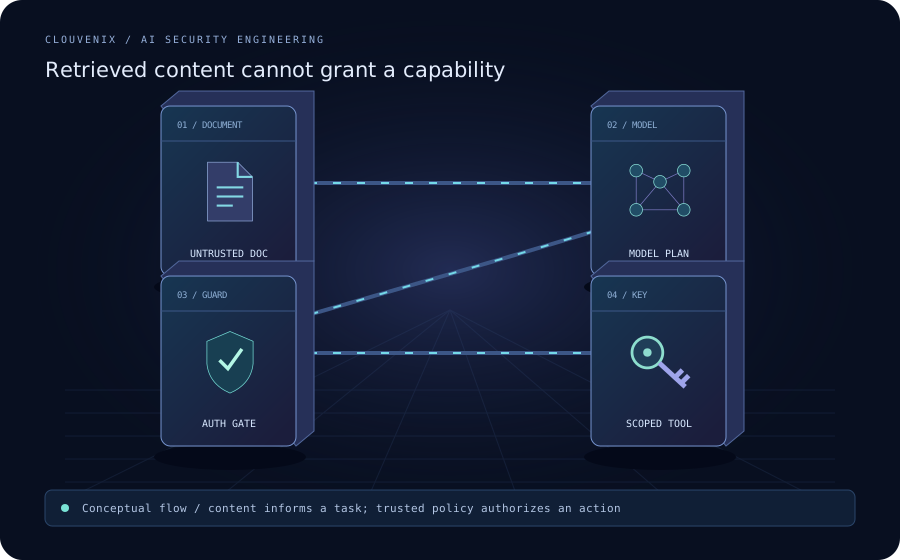 ENGINEERING JOURNAL ↗
AI tool calls: enforce authorization outside retrieved text
Design AI-assisted tools with independent authorization, narrow capabilities and adversarial tests so instructions hidden in documents cannot grant system access.
Read field note ↗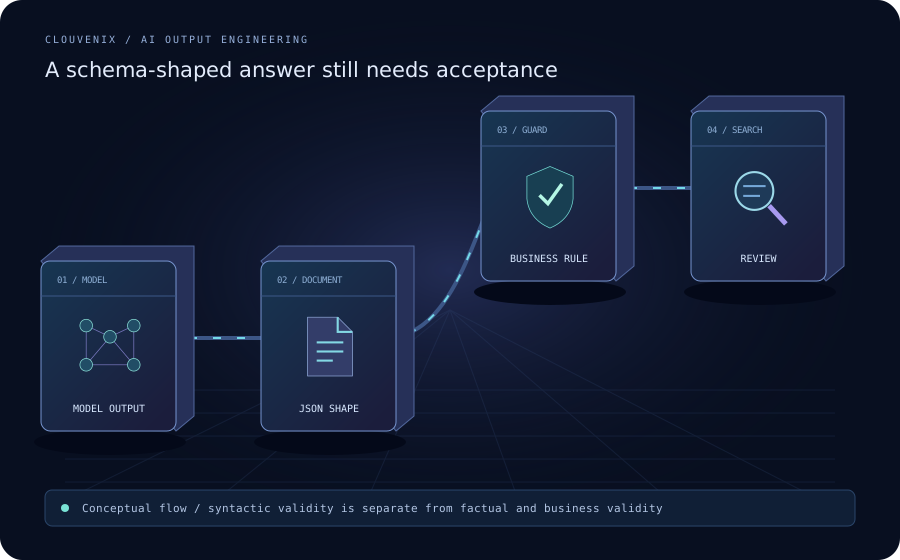 ENGINEERING JOURNAL ↗
AI structured output: validate meaning after JSON shape
Use structured AI responses with explicit schema support, semantic validation and review boundaries so valid JSON cannot silently become an invalid business action.
Read field note ↗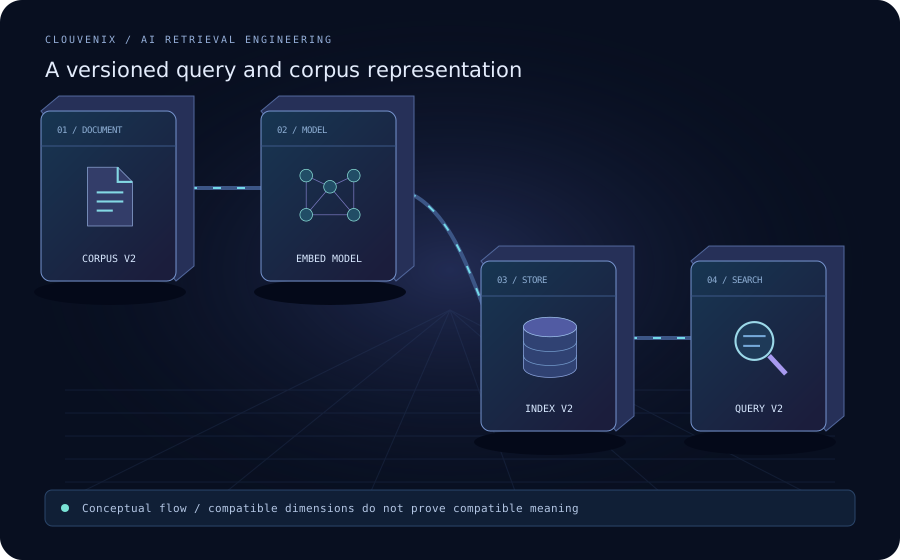 ENGINEERING JOURNAL ↗
Embedding upgrades: migrate the retrieval contract with the index
Plan an embedding-model migration using versioned corpus and query pipelines, retrieval evaluation and a reversible index switch rather than dimensions alone.
Read field note ↗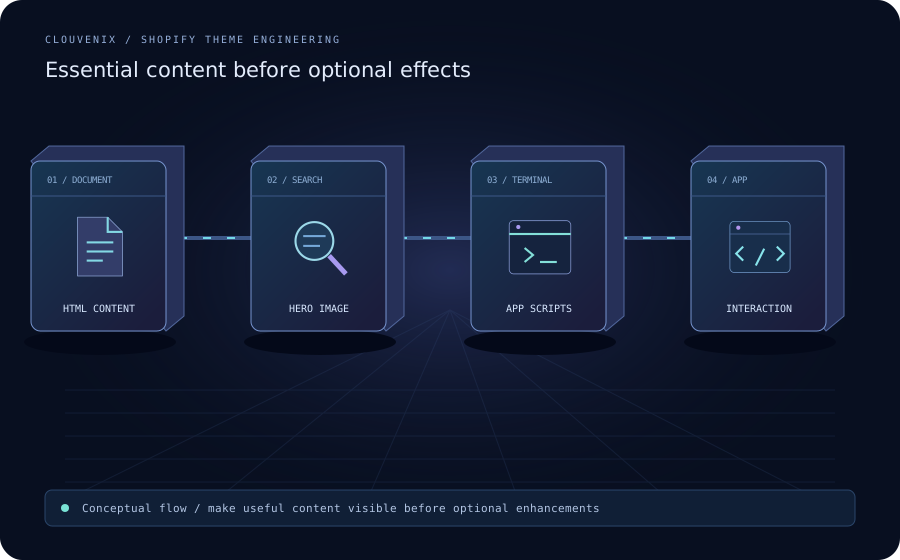 ENGINEERING JOURNAL ↗
Shopify theme performance: inspect the real rendering path
Improve Shopify theme responsiveness by tracing critical images, app scripts and main-thread work, then verify checkout-related behavior and accessible motion.
Read field note ↗ ENGINEERING JOURNAL ↗
Shopify app scopes: compare requested and granted access
Diagnose Shopify permission failures by separating declared scopes, merchant-granted access, token identity and the supported installation or reauthorization flow.
Read field note ↗ ENGINEERING JOURNAL ↗
Magento queue backlog: verify consumers and business progress
Investigate Magento asynchronous backlogs through consumer ownership, scheduler behavior and durable task outcomes before adding workers or replaying queued work.
Read field note ↗ ENGINEERING JOURNAL ↗
Magento OpenSearch: verify the application search destination
Diagnose Magento search failures by checking the configured OpenSearch endpoint, environment-specific index prefix and search acceptance beyond a connection test.
Read field note ↗ ENGINEERING JOURNAL ↗
ASP.NET Data Protection: keep a shared service consistent across nodes
Diagnose protected-cookie failures across ASP.NET Core instances by reviewing persistent key rings, application isolation and key-at-rest access without exposing secrets.
Read field note ↗