
Ideas for
your next move.
Practical thinking for teams building software, securing systems and operating modern infrastructure. Explore our engineering field notes.
500 insights · Page 12 of 42
 ENGINEERING JOURNAL ↗
systemd Credentials: Deliver Secrets as Scoped Files
Use systemd credential files to define a secret handoff, verify application compatibility and rehearse rotation without exposing secret values in diagnostics.
Read field note ↗ ENGINEERING JOURNAL ↗
systemd Environment Files: Explain Missing Service Settings
Find why a systemd service receives different settings from your shell, then validate environment files, quoting and deployment ownership safely.
Read field note ↗ ENGINEERING JOURNAL ↗
Private Google Access: verify subnet, DNS and routes
Trace Google API access from a VM without an external IP through subnet settings, API hostname resolution, routes and egress policy.
Read field note ↗ ENGINEERING JOURNAL ↗
Cloud Logging exclusions: review every routing destination
Review Cloud Logging exclusion filters against individual sinks and destination ownership so retention and cost changes preserve required incident evidence.
Read field note ↗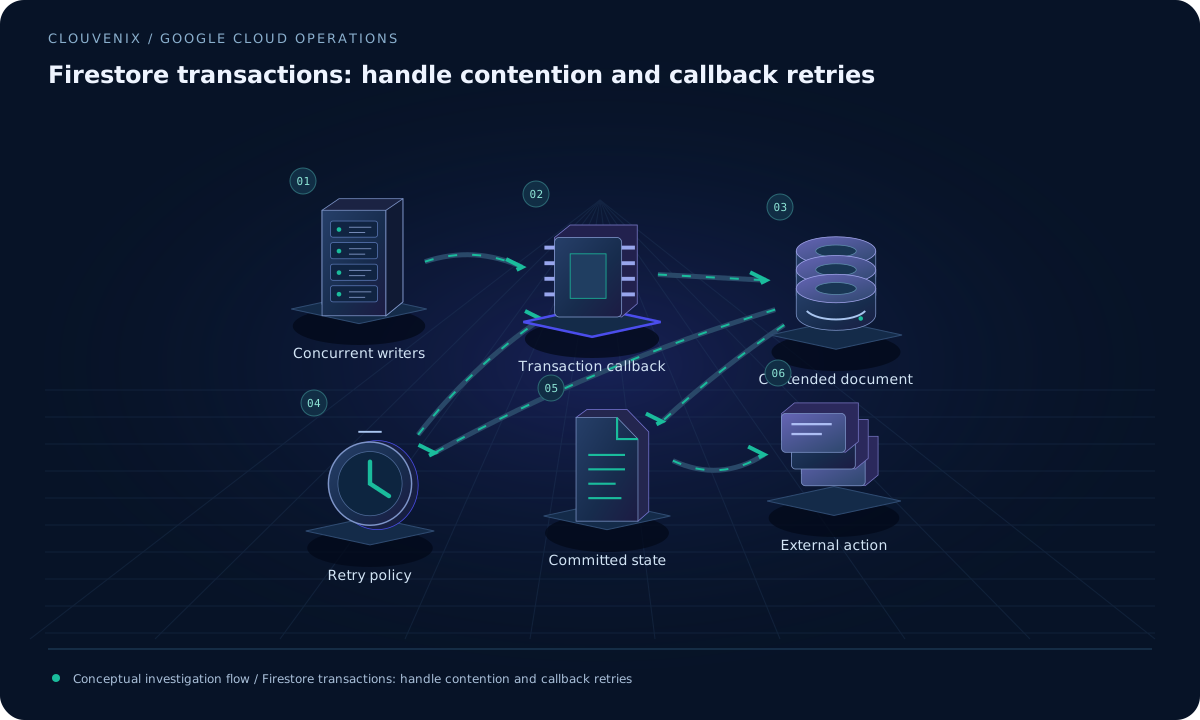 ENGINEERING JOURNAL ↗
Firestore transactions: handle contention and callback retries
Investigate Firestore transaction contention using conflicting documents and runtime semantics, then keep retried callbacks free of uncontrolled external effects.
Read field note ↗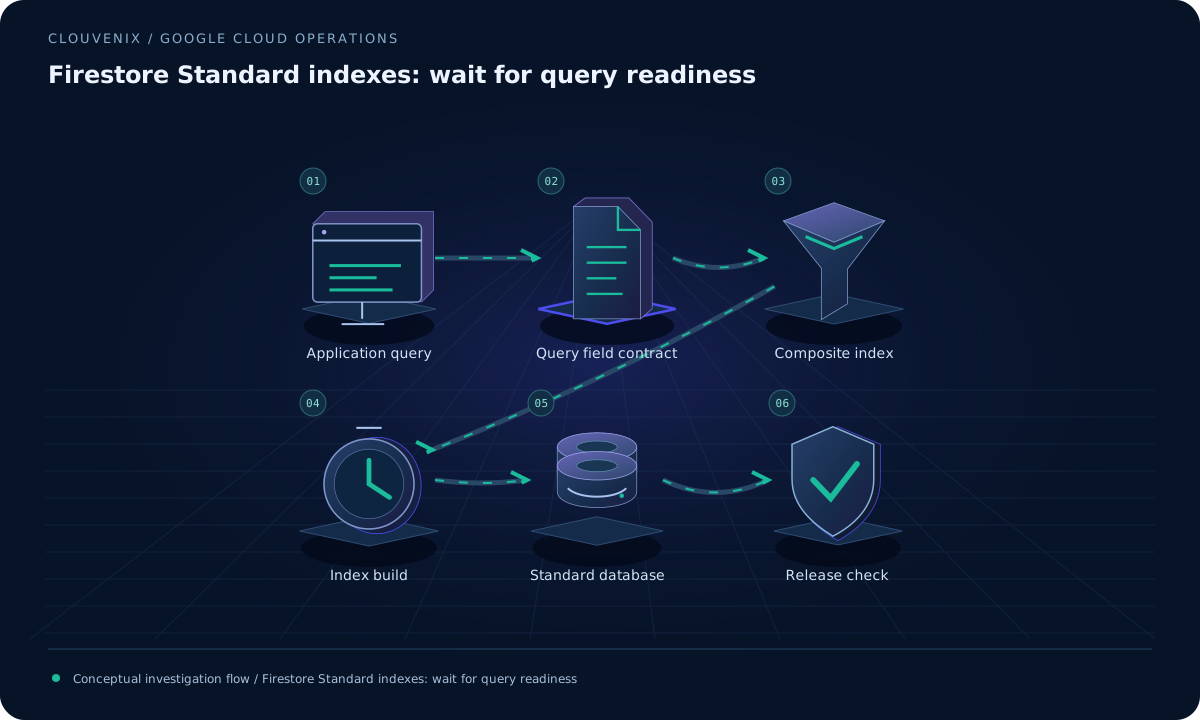 ENGINEERING JOURNAL ↗
Firestore Standard indexes: wait for query readiness
Diagnose a Firestore Standard compound query using its exact fields, collection scope, index definition and build status before releasing the feature.
Read field note ↗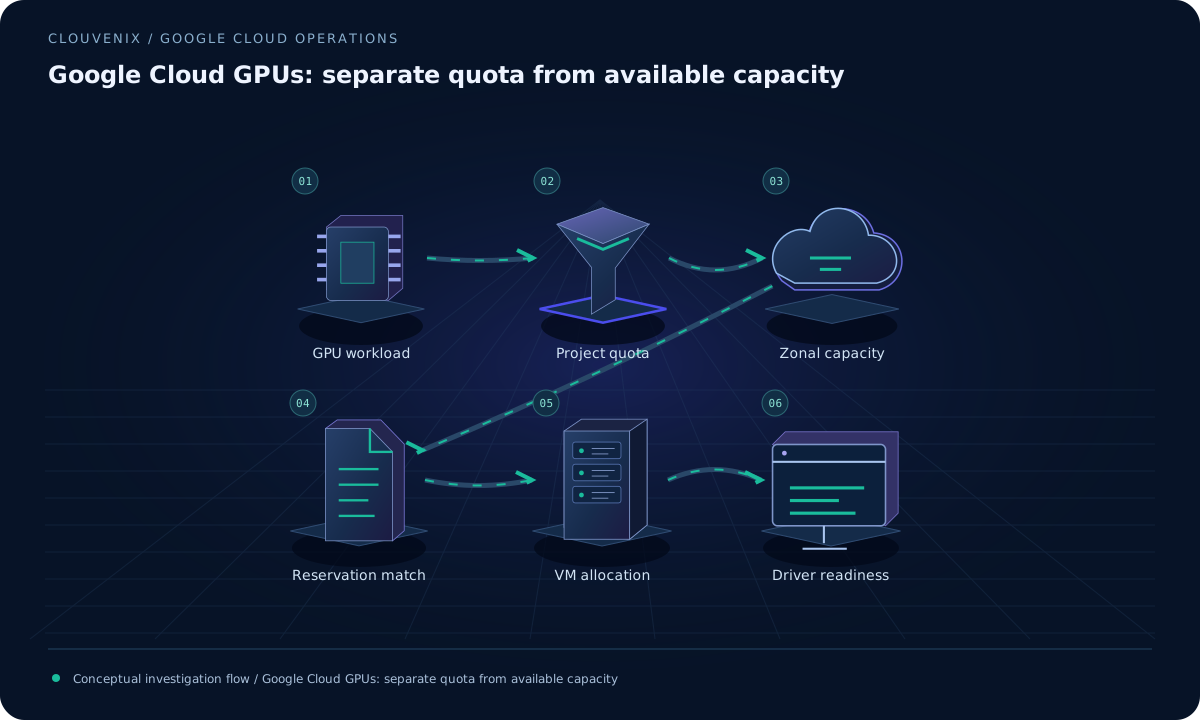 ENGINEERING JOURNAL ↗
Google Cloud GPUs: separate quota from available capacity
Diagnose GPU provisioning failures by separating quota, zonal capacity, machine compatibility and reservation matching before changing a workload.
Read field note ↗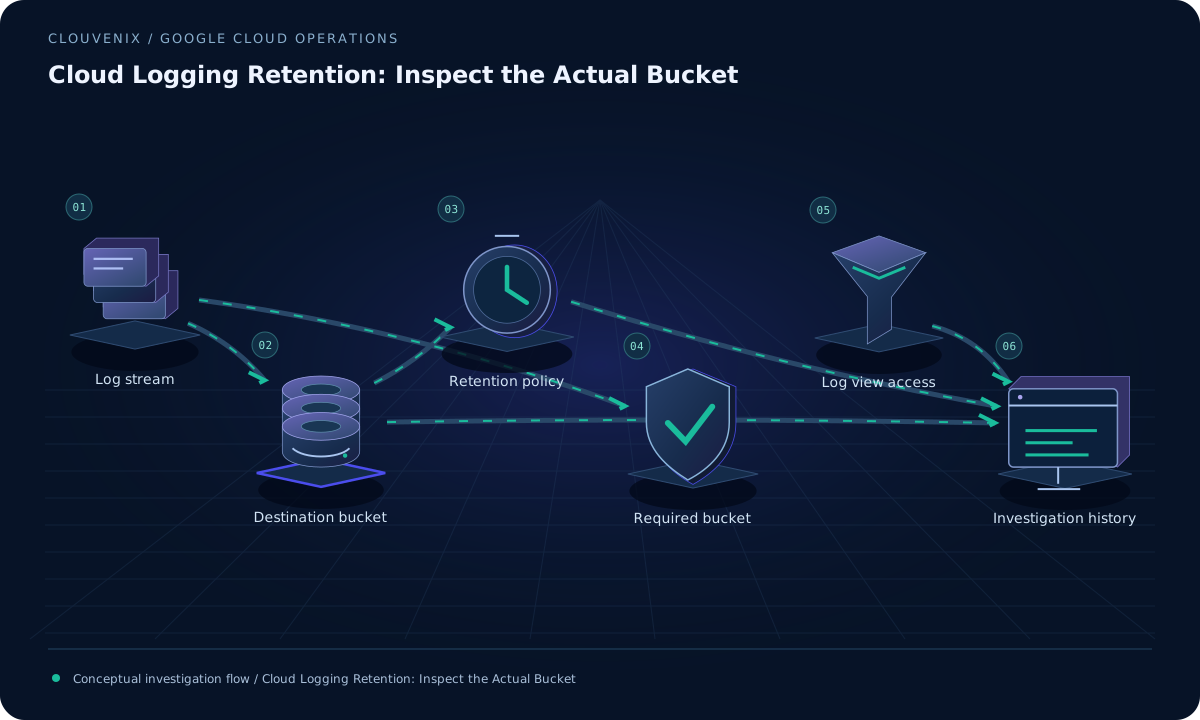 ENGINEERING JOURNAL ↗
Cloud Logging Retention: Inspect the Actual Bucket
Plan Cloud Logging retention using the destination bucket, fixed required-log policy, access views, storage cost, and the recovery limits of deleted history.
Read field note ↗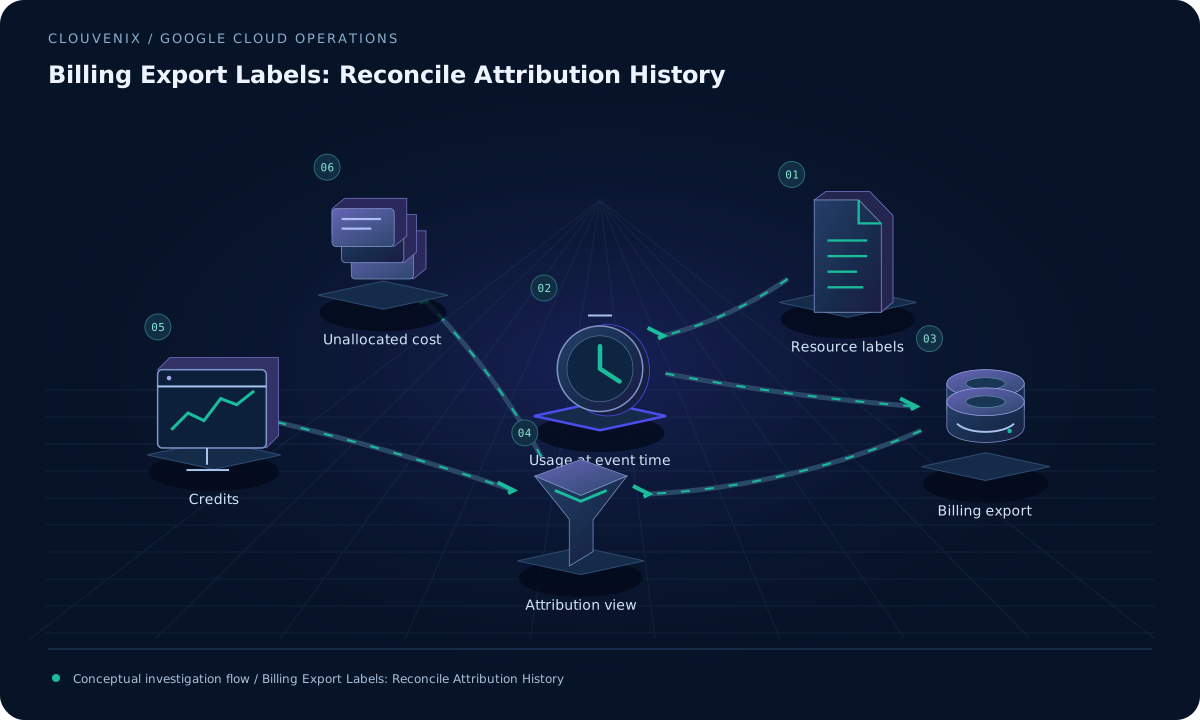 ENGINEERING JOURNAL ↗
Billing Export Labels: Reconcile Attribution History
Build reliable Google Cloud cost attribution by checking when labels took effect, export freshness, repeated fields, credits, and unallocated usage.
Read field note ↗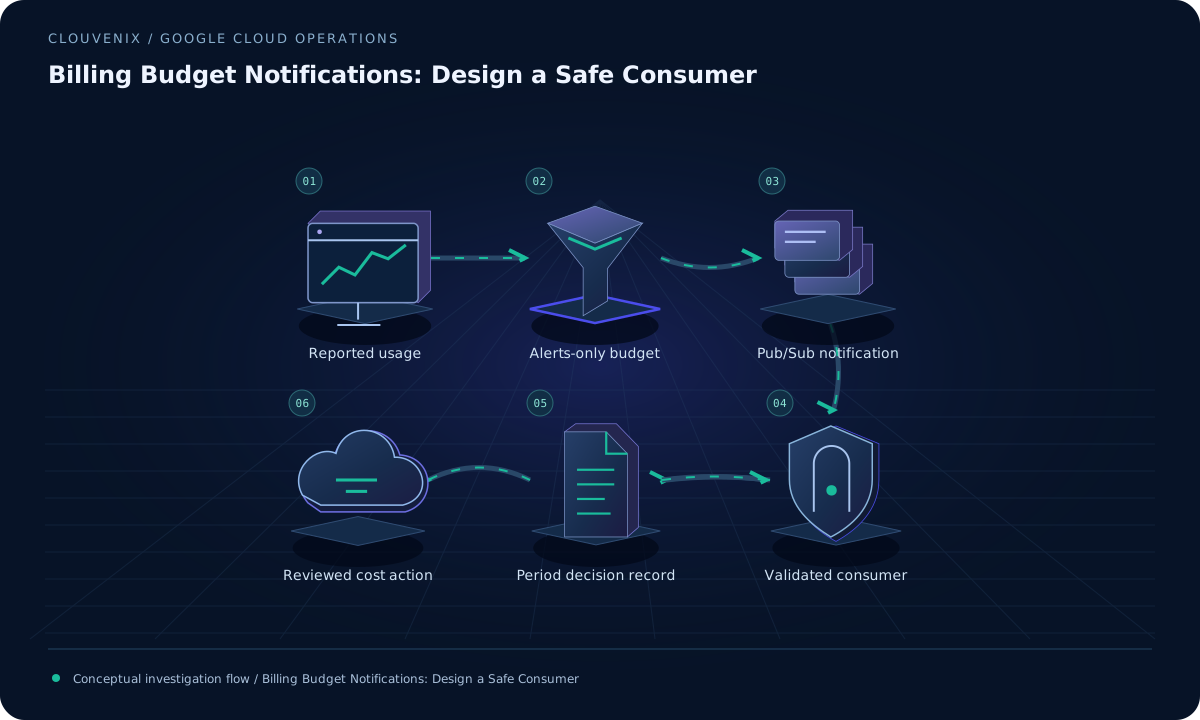 ENGINEERING JOURNAL ↗
Billing Budget Notifications: Design a Safe Consumer
Use alerts-only Cloud Billing budget notifications as delayed cost signals, with validated schemas, period-aware decisions, and reviewed resource responses.
Read field note ↗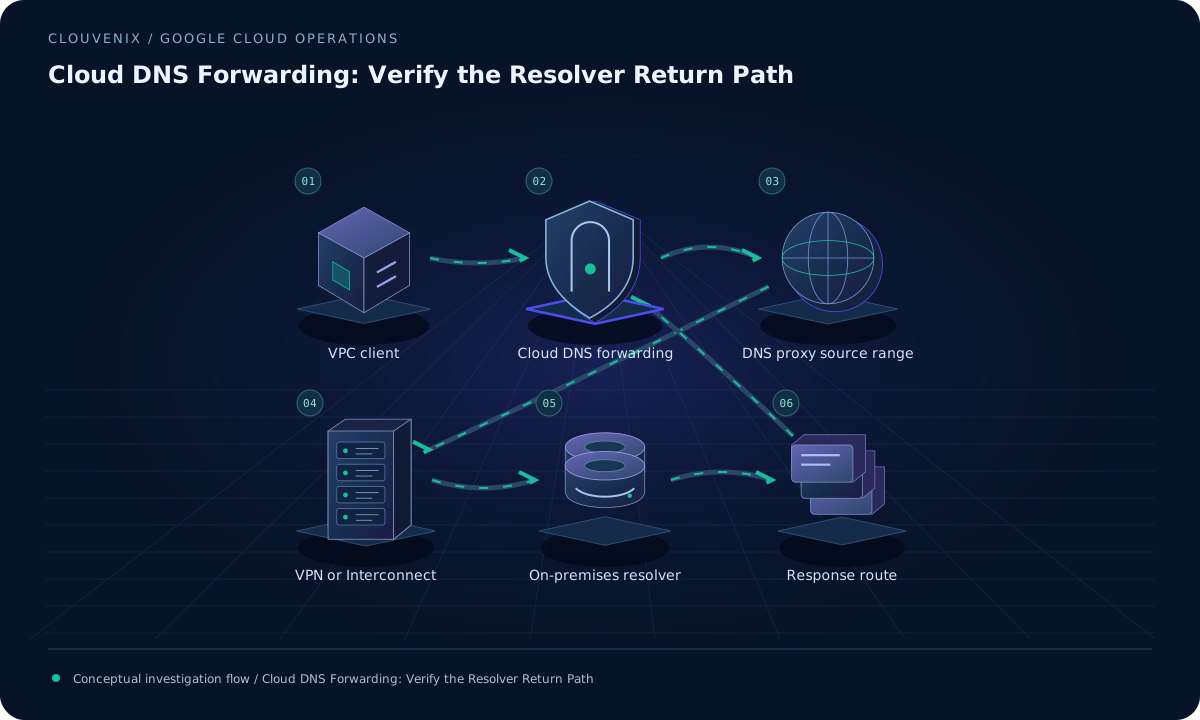 ENGINEERING JOURNAL ↗
Cloud DNS Forwarding: Verify the Resolver Return Path
Troubleshoot on-premises DNS forwarding from Google Cloud by checking the forwarding-zone target, DNS proxy source range, firewall rules, and response route.
Read field note ↗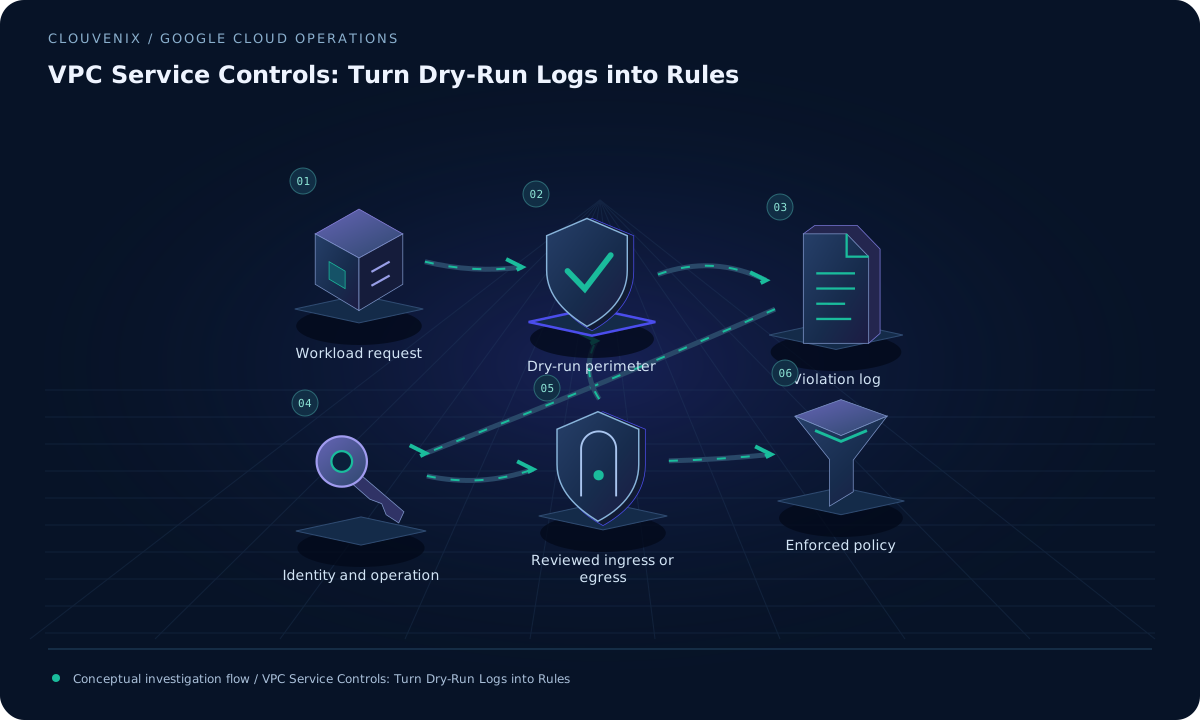 ENGINEERING JOURNAL ↗
VPC Service Controls: Turn Dry-Run Logs into Rules
Prepare a service perimeter by tracing dry-run violations to real workloads, distinguishing ingress from egress, and reviewing narrowly scoped exceptions.
Read field note ↗