
Ideas for
your next move.
Practical thinking for teams building software, securing systems and operating modern infrastructure. Explore our engineering field notes.
500 insights · Page 11 of 42
 ENGINEERING JOURNAL ↗
NetworkManager Routes: Explain the Chosen Default Path
Investigate a Linux host using the wrong outbound interface by comparing active routes, connection profiles, metrics and persistent default-route intent.
Read field note ↗ ENGINEERING JOURNAL ↗
Ubuntu Release Upgrades: Inventory Third-Party Dependencies
Prepare an Ubuntu release change by mapping third-party packages, supported upgrade paths, recovery evidence and application checks before starting the upgrader.
Read field note ↗ ENGINEERING JOURNAL ↗
APT Signature Errors: Verify the Repository Key Boundary
Troubleshoot APT repository signature failures by checking Signed-By, key fingerprints, readability and duplicate source entries without bypassing verification.
Read field note ↗ ENGINEERING JOURNAL ↗
Ubuntu Automatic Updates: Make Reboot Policy Explicit
Check which Ubuntu updates run automatically, distinguish installation from activation and define a reboot procedure that fits your application availability needs.
Read field note ↗ ENGINEERING JOURNAL ↗
Auditd Backlogs: Detect Lost Evidence Before Tuning
Interpret Linux audit backlog and lost-record counters, investigate the consumer and storage path, and validate a correction without clearing useful evidence.
Read field note ↗ ENGINEERING JOURNAL ↗
Rsyslog TLS Forwarding: Follow Delivery and Queue Evidence
Separate rsyslog TLS authentication from queueing and remote ingestion, then verify a harmless message reaches the intended logging destination.
Read field note ↗ ENGINEERING JOURNAL ↗
Logrotate and Daemons: Verify the Reopen Contract
Build a reliable log rotation procedure by checking application reopen support, file ownership and postrotate behavior with a controlled marker test.
Read field note ↗ ENGINEERING JOURNAL ↗
OpenSSH FIDO Keys: Test Presence, PIN and Recovery
Plan an OpenSSH security-key rollout by checking supported key types, user presence, PIN behavior and a recoverable enrollment workflow before relying on hardware.
Read field note ↗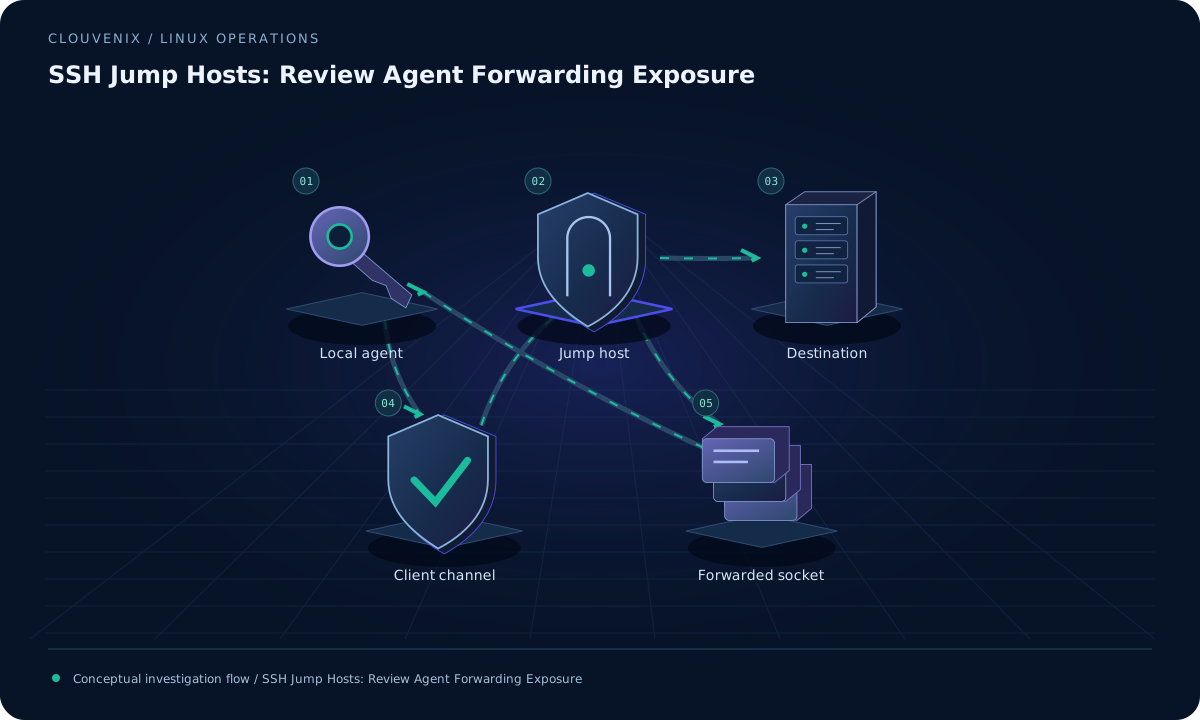 ENGINEERING JOURNAL ↗
SSH Jump Hosts: Review Agent Forwarding Exposure
Understand what SSH agent forwarding exposes on an intermediate host and test a ProxyJump workflow with explicit destinations and verified host identities.
Read field note ↗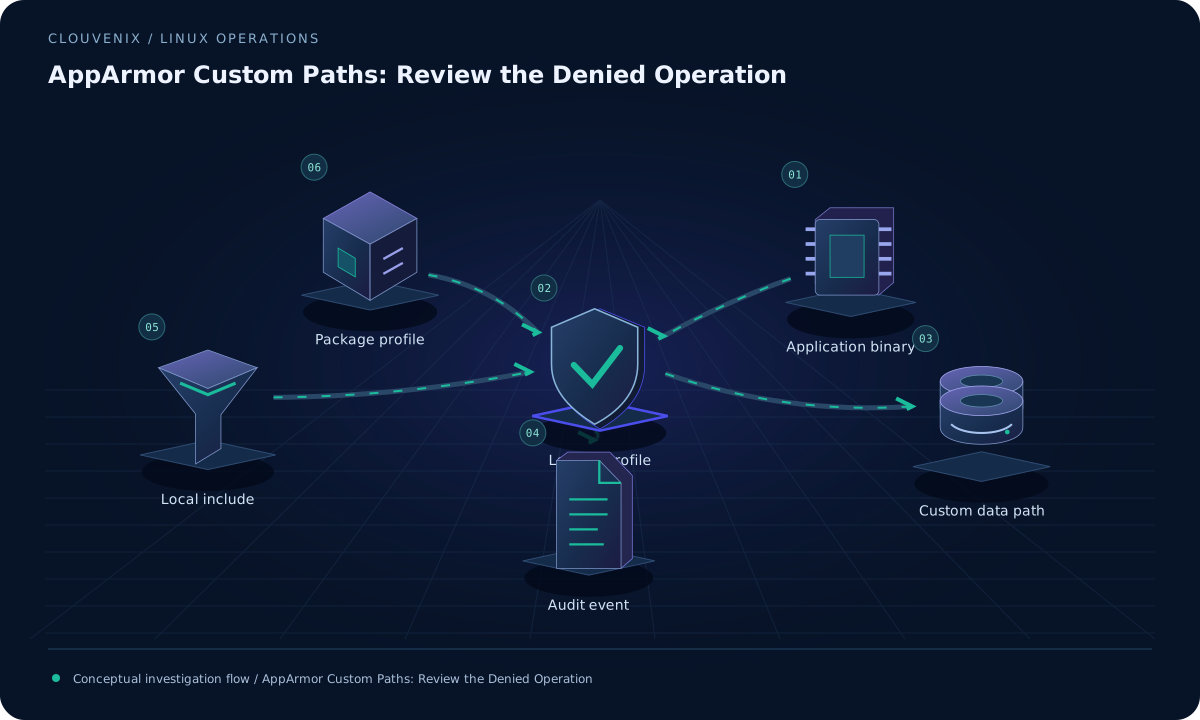 ENGINEERING JOURNAL ↗
AppArmor Custom Paths: Review the Denied Operation
Connect an AppArmor denial to the responsible profile, review a custom data path and preserve a narrow local policy through application and package changes.
Read field note ↗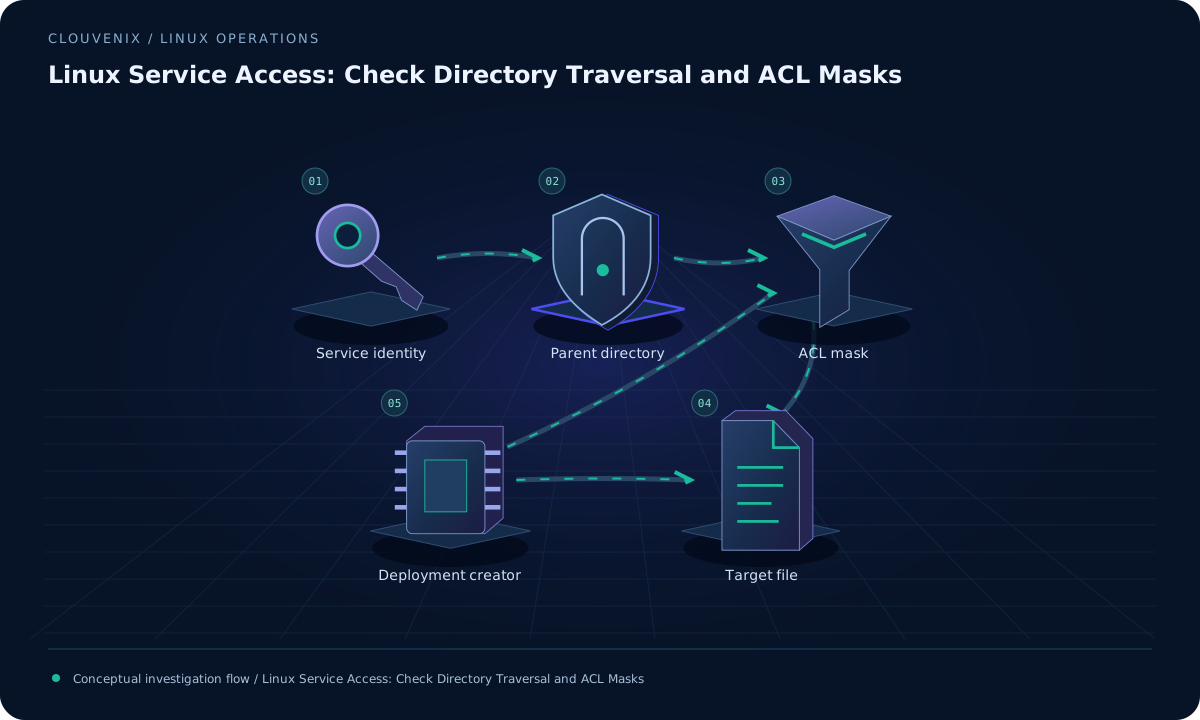 ENGINEERING JOURNAL ↗
Linux Service Access: Check Directory Traversal and ACL Masks
Investigate a service that cannot read a file even when its file mode looks correct by checking parent directories, group membership and effective ACL entries.
Read field note ↗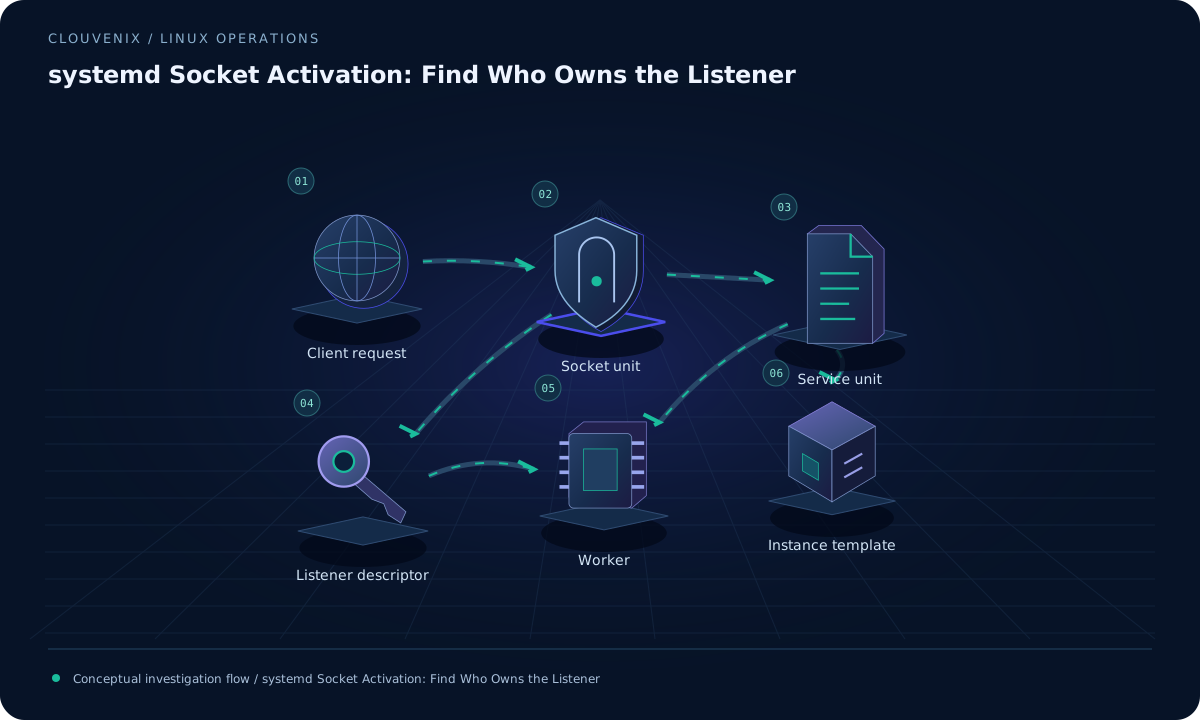 ENGINEERING JOURNAL ↗
systemd Socket Activation: Find Who Owns the Listener
Trace a socket-activated service from its listening unit to the application, and explain port conflicts or surprising activation without killing unrelated processes.
Read field note ↗